Ledger confirms a hardware implant incident
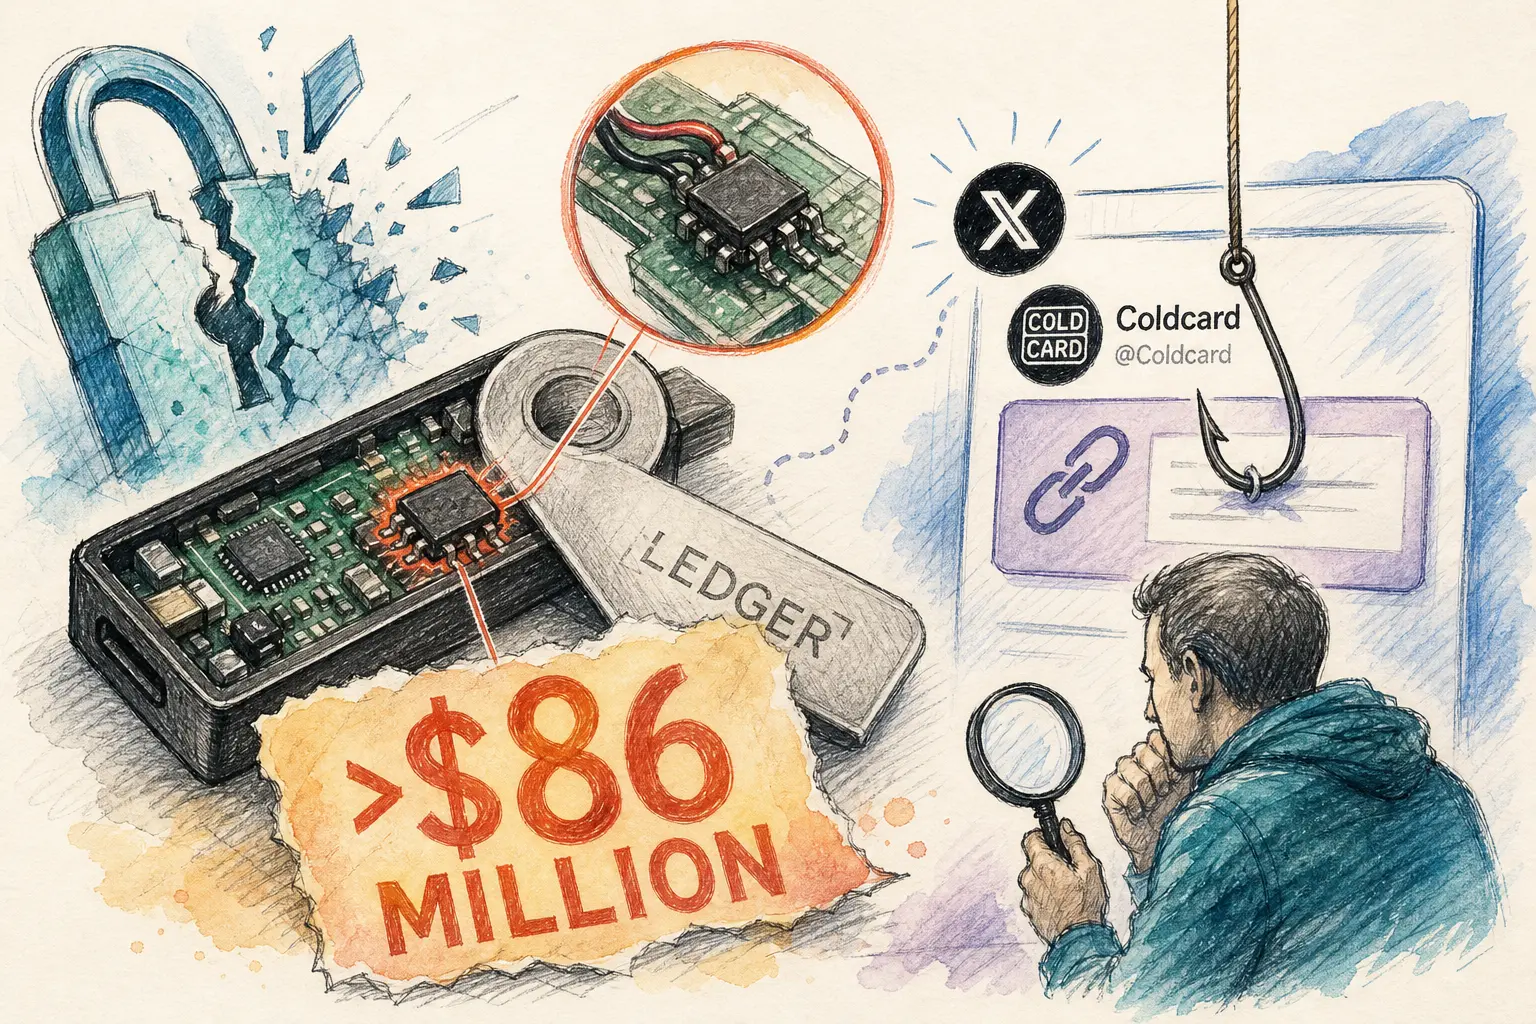
Ledger has confirmed that an unauthorized hardware implant was discovered, and it says the financial impact could exceed $86 million. The company has not yet fully explained how the device was compromised, but the confirmation raises immediate questions about supply-chain security and hardware trust.
Why this matters
A hardware implant is an unauthorized component or modification added to a device, often with the goal of altering its behavior or creating a security weakness. In products that are meant to protect digital assets, even a small hardware change can have outsized consequences because users rely on the device to keep sensitive keys or transactions secure.
Separate concern: Coldcard’s X account
In a related but distinct incident, Coldcard says it is investigating how a phishing link appeared on its X account. A phishing link is a fraudulent link designed to trick users into revealing credentials or sending money to an attacker.
That investigation is still ongoing, and the available information does not establish whether the account issue is connected to Ledger’s incident.
What readers should take away
- Ledger has acknowledged an unauthorized hardware implant.
- The company says losses may be greater than $86 million.
- Coldcard is separately looking into a phishing link posted through its X account.
- At this stage, the two incidents should be treated as separate reported events unless further evidence links them.